We built the firm we wish we'd been able to hire.

We'd lived the problem ourselves. Smaller organizations get two bad options: enterprise consultants priced for companies ten times their size, or a pile of tools and a login, with all the actual work still landing on someone who already has a job.

Neither one gets you compliant. Neither one leaves you able to prove it. So we built the alternative — software that turns requirements into assigned work, and credentialed practitioners who review it before anyone external does.

Veteran-ownedSBA-certified small business · CAGE 9WVS6
Cyber AB RPA-ledRegistered Practitioner Advanced, credentialed by the Cyber AB
Compliance is all we doNot a generalist IT shop with a compliance line
Not a C3PAOWe prepare you — we don't grade you. That separation keeps your evidence defensible.

We exist to make a real compliance program affordable at your size.

Small and mid-sized organizations carry the same requirements as companies ten times larger, with none of the staff. A defense supplier, a CPA firm, a healthcare vendor and a SaaS company face very different regulators and end up in exactly the same position: somebody has to do the work, and that somebody already has a job.

Being compliant shouldn't demand a full-time hire, an enterprise budget or six months of disruption — and proving it shouldn't cost more than the contract is worth. Technology carries the volume. Credentialed practitioners make the calls that need judgment.

We own the outcome We don't hand you a checklist and walk away. We run the program and answer for the result — the work completed and the evidence that holds up.
Straight answers You'll know what's in scope, what isn't, and what it costs before you sign anything. If you're not ready, or we're not the fit, we say so.
No lock-in What we build is yours — your tenant, your accounts, your documentation. If you leave, all of it comes with you.
Built for the mission Greypike is veteran-founded. We don't backdate evidence and we don't fabricate artifacts — the people depending on your work deserve better than a paper program.

The mission continues.

The uniform comes off. The mission never ends.

Built by people who've been there.

Veterans, cybersecurity professionals and compliance practitioners who understand both the mission and the technical requirements.

David Dillow, Founder and CTO of Greypike

David Dillow

Founder · CTO

Founder of Greypike and architect of the Secure Enclave. Deep experience in secure cloud infrastructure, GCC High and Google Assured Workloads environments, and the technical implementation of NIST 800-171 controls.
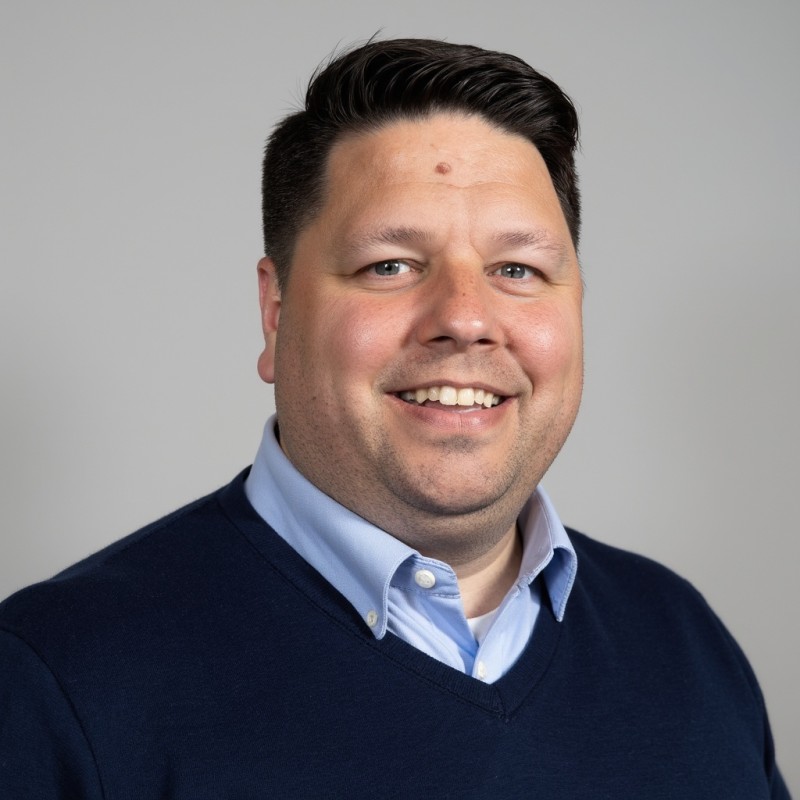
U.S. Military Veteran
Rob Sinex, Co-Founder and CEO of Greypike

Rob Sinex

Co-Founder · CEO

Leads client strategy and compliance program delivery, pairing a strong cybersecurity background with technology leadership. Focused on giving smaller organizations a real compliance program without the enterprise price tag.

Cyber AB Registered Practitioner Advanced
Brandon Poe, Lead Engineer at Greypike

Brandon Poe

Lead Engineer

Supports Greypike's AI enablement work and the broader technical engineering across client environments — from enclave configuration to secure integrations. Brings hands-on FedRAMP experience to how Greypike builds and hardens compliant systems.
U.S. Military Veteran

What we stand on.

Five centuries ago, pikemen held the line through discipline, not noise. The same principles shape how we work today — every engagement, every environment, every client.

Hold the line
Compliance isn't a milestone you pass and forget. We plant ourselves in front of your program and stay there — through audits, through affirmations, through the requests that never stop. We don't move.
Own the outcome
We don't hand you a checklist and wish you luck. We take responsibility for the result — the work completed, the evidence collected, the review done — and measure ourselves by whether you can actually prove it when somebody asks.
Real work, not checkbox compliance
A passing score that doesn't reflect how you operate isn't a win — it's a liability with a certificate attached. We build programs that hold when tested, with compliance as the proof rather than the point.
Operate in the grey
The hard problems don't live in black and white. They live in the grey — where requirements are ambiguous, scopes are messy, and the honest answer is "it depends, and here's on what." It's the ground our veterans operated on in uniform, and it's where this team works best.

Built for the organizations the big firms overlook

We started in the Defense Industrial Base and that's still where the hardest version of this problem lives. The same shape turns up in accounting firms, healthcare vendors, manufacturers and software companies — requirements written for someone with a compliance department, landing on someone who hasn't got one.

TICK WHAT'S TRUE OF YOU

Tick anything that applies0OF 6
We may not be the fit if…
×You're a large enterprise with a full in-house compliance team — you'll be better served by a platform built for them.
×You need a C3PAO to perform your certification assessment, or a CPA firm to issue a SOC 2 report. Those are separate, independent roles by design.
×You want a passing score without changing anything about how you actually operate. We won't help with that, and we'd rather say so now.

Why you can trust us with this

Credentials that can be checked, and limits we state plainly.

Veteran-Owned Small BusinessSBA-certified · CAGE Code 9WVS6 · registered in SAM.gov
Cyber AB Registered Practitioner AdvancedOur CMMC practice is RPA-led. The credential is held individually by Rob Sinex.
Microsoft GCC High deploymentAOS-G partner through Pax8 — we deploy and manage Microsoft 365 GCC High in a tenant you own.
CMMC Level 2 — self-assessedWe hold ourselves to the same NIST 800-171 standard we deliver for clients.
CAGE 9WVS6SAM UEI N6CJNGDARFM5DUNS 132171639

See if we're the right fit.

You've seen who we are and how we work. The next step is a conversation — tell us what you handle and what your customers are asking for, and we'll tell you honestly whether we can help.

Veteran-founded · Cyber AB RPA-led · Compliance is all we do